# 2026-05-19 New feature: filter holder groups at the IdP login

### The new feature

<p class="callout info">From now on, the **service providers** who have selected the “**Ask for group membership after authentication**” option will be able to filter which of these should be selectable with the attribute "**Script to filter out group memberships**".</p>

### Bear in mind

Please note the following points:

- The **holder groups** **must be** correctly **configured** in Soffid.
- If there is only **one** possible **holder group**, it is **selected automatically** and is not displayed to the user.

### How to configure it?

The following **components** must be installed:

- Addon federation 4.0.25 (or higher)

In a later release, further attributes have been added to the script:

- Addon federation 4.0.40 (or higher)

<p class="callout info">The [Service Providers](https://bookstack.soffid.com/books/soffid-4-reference-guide/page/service-providers-addon-federation#bkmrk-login-rules) reference page lists the attributes that can be used.</p>

### Let's look at an example

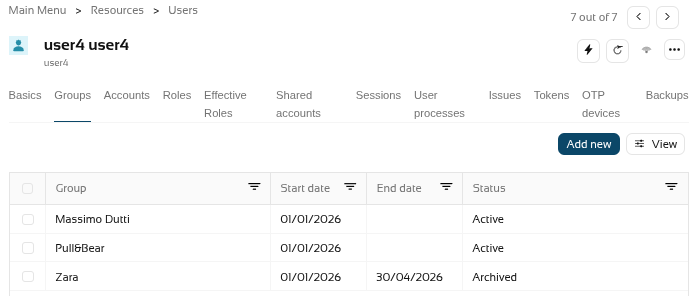
Let’s look at an example, here we have the user "**user4**" who has already set up the **holder groups**.

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/JpAKXBOb9tYRKvLA-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/JpAKXBOb9tYRKvLA-image.png)
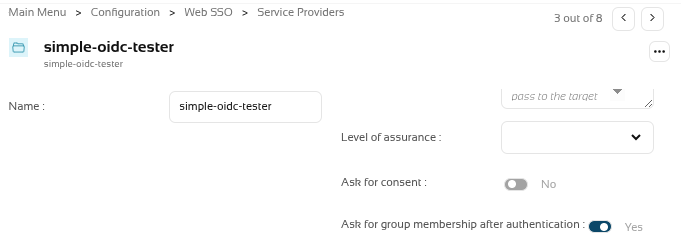
We had a **service provider** that was already selected the option "**Ask for group membership after authentication**".

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/kP8QV9hPqFVt8sdA-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/kP8QV9hPqFVt8sdA-image.png)
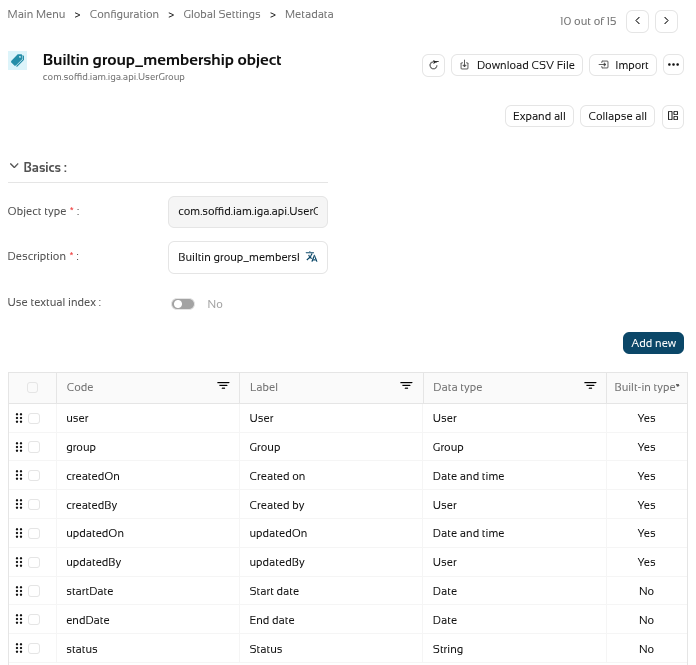
The holder groups have several **custom attributes** (startDate, endDate and status).

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/jSgdoRMeh0qAllS1-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/jSgdoRMeh0qAllS1-image.png)
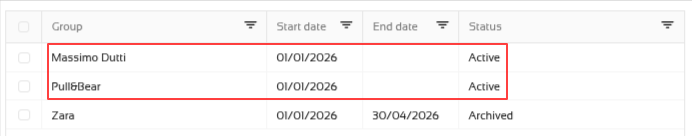
We now want to **filter** the **holder groups** with the attibute **status** with the **Active** value.

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/YqrDoi5j8iFQ3WLV-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/YqrDoi5j8iFQ3WLV-image.png)
So we're going to create a script in the "**Script to filter out group memberships**" of the service provider.

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/9PjFDOz2srel64TD-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/9PjFDOz2srel64TD-image.png)
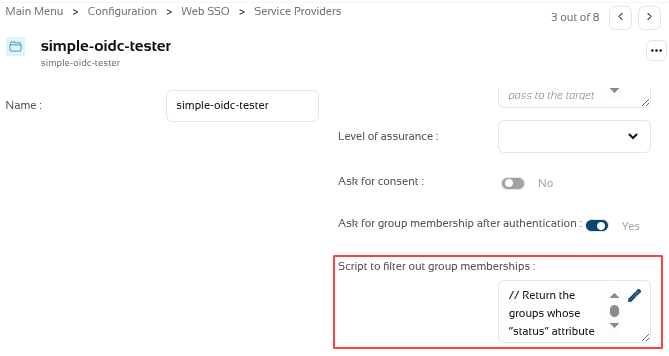
This is the script.

```
// Return the groups whose “status” attribute has the value "Active"
//
l = new java.util.ArrayList();
lug = serviceLocator.getGroupService().findUsersGroupByUserName(user.userName);
for (i=0; i<lug.size(); i++) {
  ug = lug.get(i);
  if (ug.attributes!=null &&
      ug.attributes.get("status")!=null &&
      "Active"===ug.attributes.get("status"))
  {
    l.add(ug.group);
  }
}
return l;
```

<p class="callout warning">Please note that if the **script fails** or is **not configured correctly**, the holder groups page will **not be displayed**.</p>

Now, to test it, we’ll log in to the application (the service provider), and these are the IdP’s login pages

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/ljIO7Xg3gF9ZXiLx-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/ljIO7Xg3gF9ZXiLx-image.png)

[![image.png](https://bookstack.soffid.com/uploads/images/gallery/2026-05/scaled-1680-/ZZ0FVGgc0tVBYgrq-image.png)](https://bookstack.soffid.com/uploads/images/gallery/2026-05/ZZ0FVGgc0tVBYgrq-image.png)

### About the attributes we can use

Here is a brief example of a script that we can use to return a specific group based on the additional data.

```bash
externalWithPermissions = false;
if (accountName.contains(".") && "Extranet".equals(serviceProvider) && "PO".equals(authenticationMethod)) {
  externalWithPermissions = true;
}

l = new java.util.ArrayList();
lug = serviceLocator.getGroupService().findUsersGroupByUserName(user.userName);
for (i=0; i<lug.size(); i++) {
  ug = lug.get(i);
  if (ug.attributes!=null && ug.attributes.get("external")!=null && "false"===ug.attributes.get("external")) {
    l.add(ug.group);
  } else if (ug.attributes!=null && ug.attributes.get("external")!=null && "true"===ug.attributes.get("external") && externalWithPermissions) {
    l.add(ug.group);
  }
}
return l;
```

Here another example:

```bash
l = new java.util.ArrayList();

log.info("accountName: "+accountName);
if (!authenticationMethod.contains("P"))
  accountName = null;

if(accountName!=null && accountName.equals(user.getAttributes.get("loginInternal")))
  l.add("INTERNAL");
else if (accountName!=null && accountName.equals(user.getAttributes.get("loginExternal")))
  l.add("EXTERNAL");
else if (accountName == null){
  l.add("ANONYMOUS");
}

log.info("l: " + l);
return l;
```